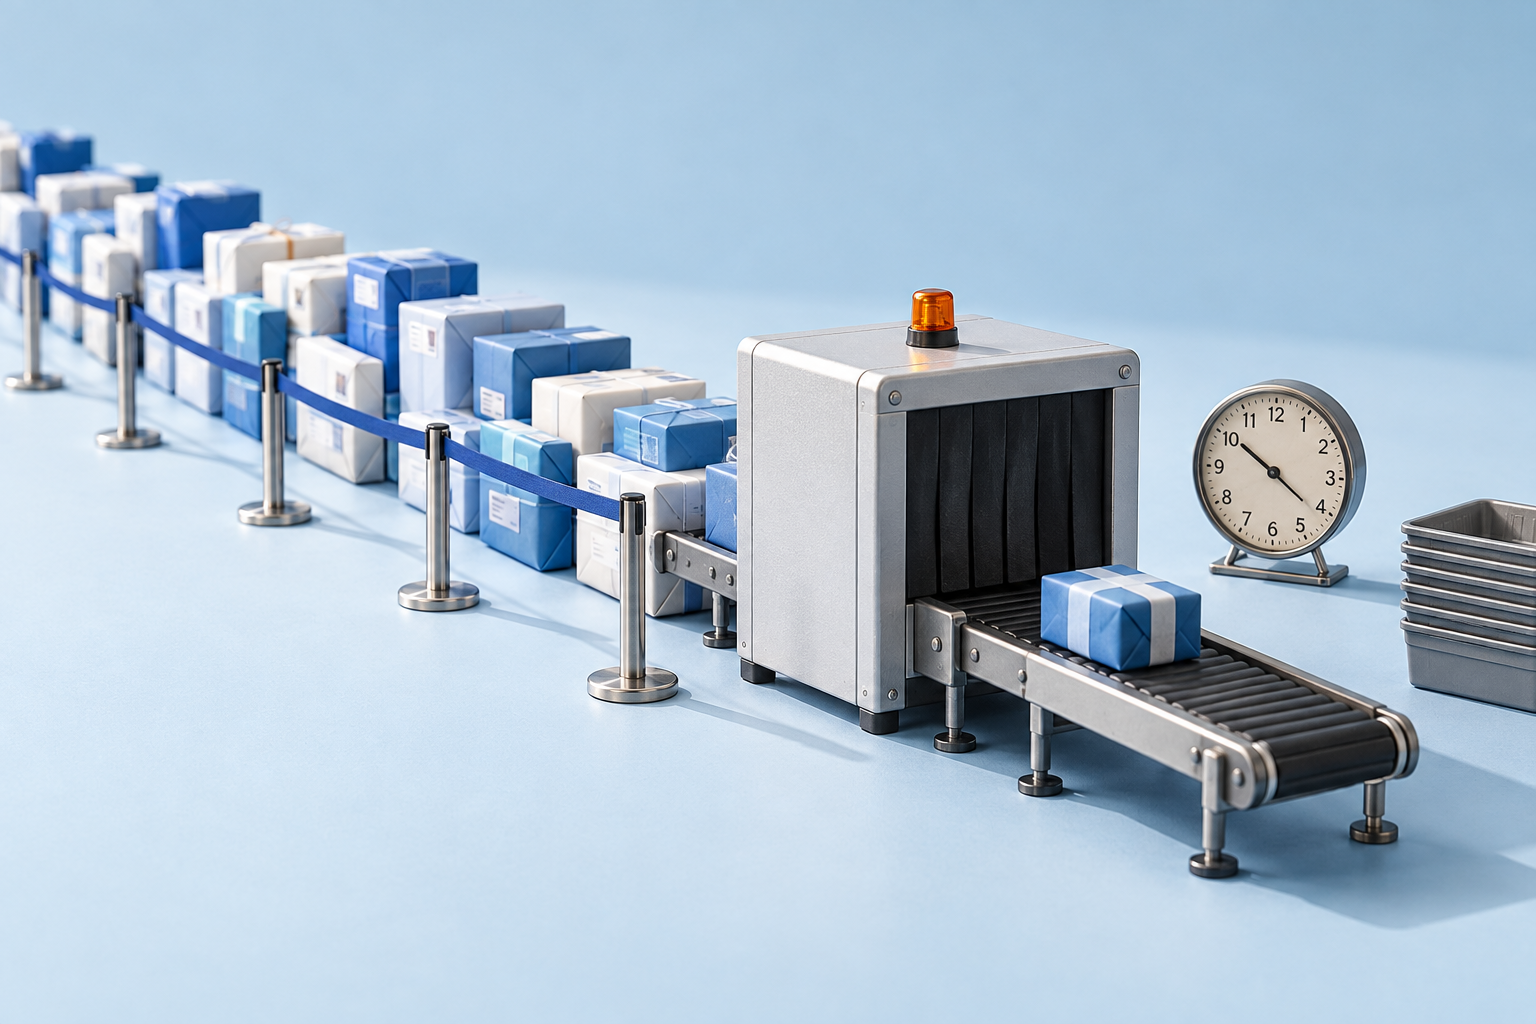
The bullshit of slow SAST scans
A security scan that keeps developers waiting can undermine the workflow it is supposed to protect. I look at feedback time, useful pipeline gates and the cost of noisy results. Faster checks should help teams act on real findings, without quietly removing the security coverage they need.